


In November 2015 we first released our MacOS sandbox. We now have an incremental feature improvements live on our site to help our users get further behavioral information from samples scanned with VirusTotal
Several improvements visible to users are:
To view the detailed behavior report, click on the behavior tab, then select the Box of Apples sandbox, then click on the detailed report link
Some Samples that might be interesting, that contain the new features:
ec7241a6009f1fff38b481d8b4fd6efede4cc2f9d8ee20d9ca2b4ff66d656171
3b196c1c1a64aca81dec5a5143b3f2faaadcc4034b343f46f23348f34a2ef205
694c23b548249056bf90b2b2c252a8c9abfae4aeb611476cbdaa8dc112f79d8f
This is part of the Multi-Sandbox project. We’ll continue to improve our own and 3rd party sandbox providers that wish to integrate sandboxes into VirusTotal.
If you find any issues, or have feature requests, please don’t hesitate to reach out to us by emailing contact@virustotal.com
Several improvements visible to users are:
- Sandbox updated to OSX 10.11 El Capitan in sandbox. We have a High sierra update planned for later this year.
- Detailed HTML analysis report is now available.
- Screenshots of the software under analysis to provide more contextual information:
- Show screenshots of what a user would see
- Help determine if the sample is waiting for user input
- Network traffic reports updated
- Country Detection
- Timestamps on file operations, to help show the sequence of events.
- Process tree is shown if there is more than one level of processes
To view the detailed behavior report, click on the behavior tab, then select the Box of Apples sandbox, then click on the detailed report link
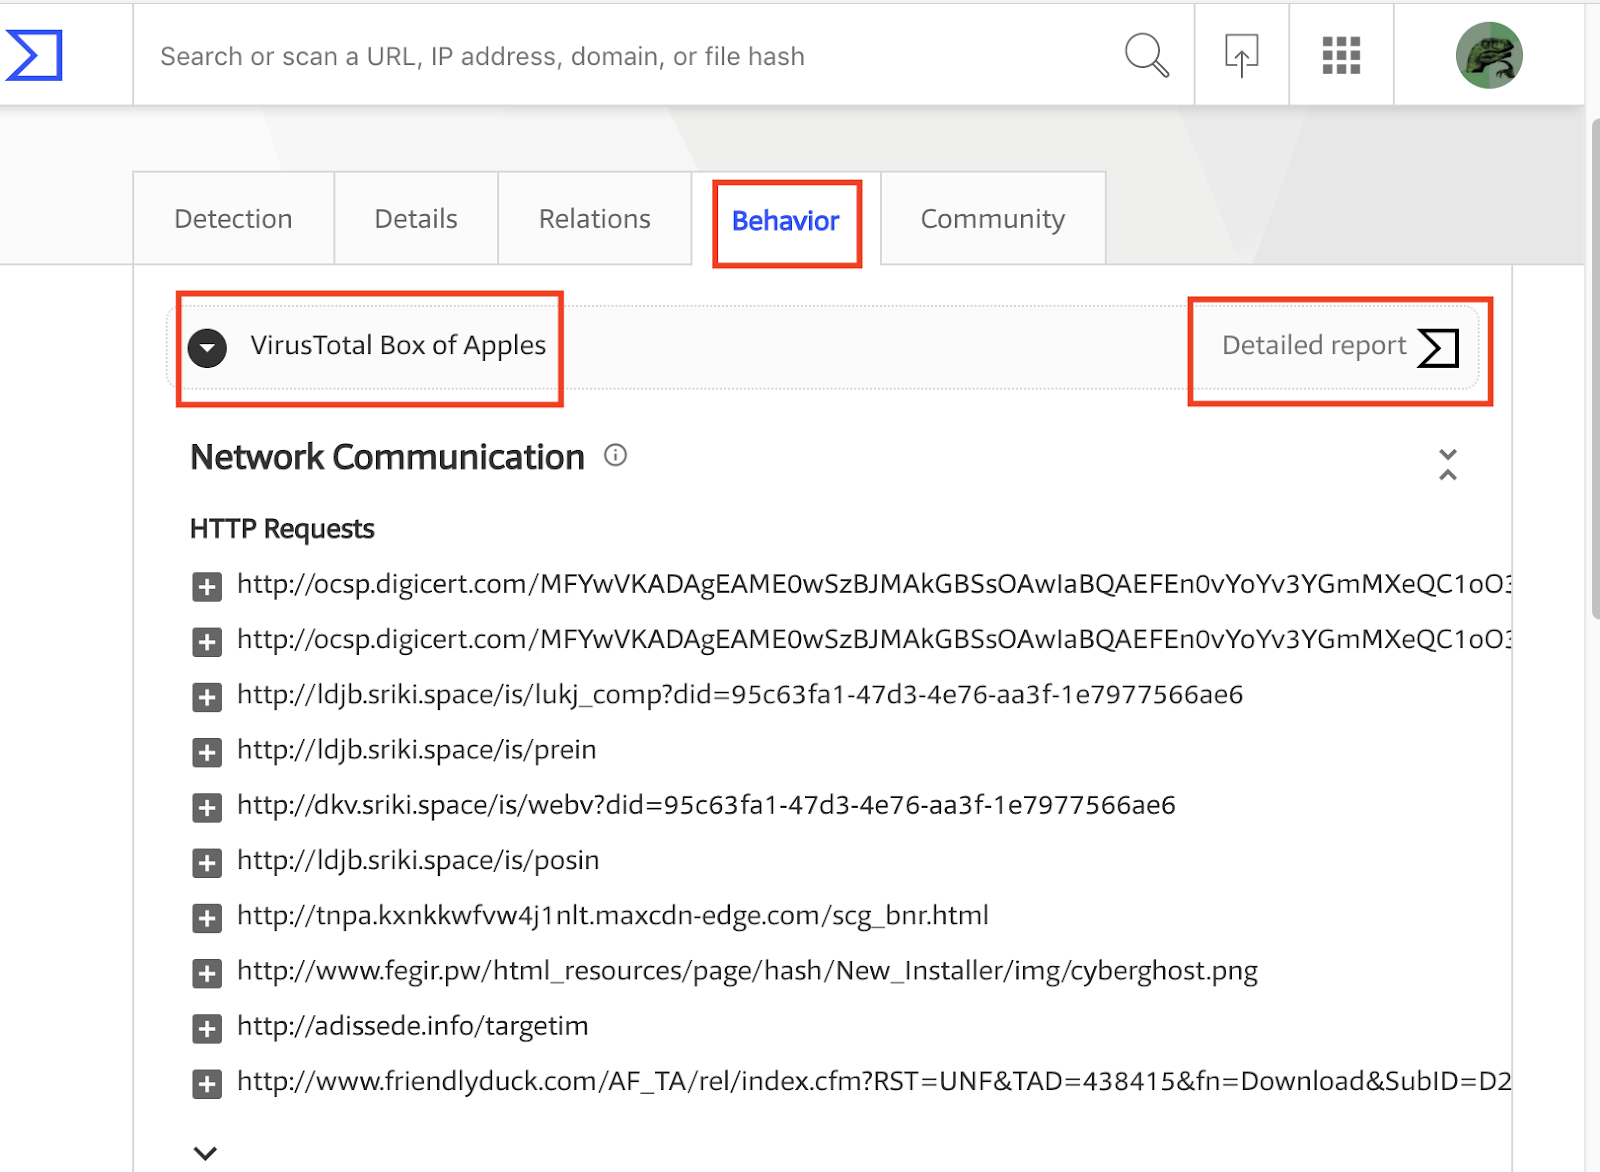 |
| Click on the detailed behavior report. |
Some Samples that might be interesting, that contain the new features:
ec7241a6009f1fff38b481d8b4fd6efede4cc2f9d8ee20d9ca2b4ff66d656171
3b196c1c1a64aca81dec5a5143b3f2faaadcc4034b343f46f23348f34a2ef205
694c23b548249056bf90b2b2c252a8c9abfae4aeb611476cbdaa8dc112f79d8f
 |
| Screenshots and File operations |
 |
| DNS, IP Traffic and Behavior tags |
This is part of the Multi-Sandbox project. We’ll continue to improve our own and 3rd party sandbox providers that wish to integrate sandboxes into VirusTotal.
If you find any issues, or have feature requests, please don’t hesitate to reach out to us by emailing contact@virustotal.com
